

Every minute a cyberattack goes unnoticed is a minute the attacker spends inside — reading emails, copying databases, planting ransomware. For most security teams, the gap between an attack beginning and anyone noticing is measured in days or weeks; the industry average for spotting a breach runs into months. A Hyderabad company built its whole platform around shrinking that gap to two minutes. That company is BluSapphire.
BluSapphire Cyber Systems was founded in 2014 by Kiran Vangaveti, and its answer is OnePlatform — a unified, AI-native security operations platform that brings SIEM, endpoint detection and response, security orchestration and automation, extended detection and response, network detection, user-behaviour analytics, threat intelligence and deception together in a single system, built from the ground up instead of stitched together from acquisitions. The company says more than 500 enterprises across banking, healthcare, manufacturing, government and technology now run on it — including stock exchanges, nuclear establishments, defence organisations, hospitals and Fortune 500 companies.
One platform instead of a dozen tools
The problem BluSapphire set out to solve is one every security team knows: too many tools, each watching a different corner, none of them talking to each other. A typical enterprise security stack is a dozen point products bolted together, each with its own console, its own alerts and its own blind spots — and a shortage of skilled analysts to watch them all. BluSapphire’s bet was that the fix is not another tool, but one platform that replaces the whole stack: a single federated architecture where detection, investigation and response share the same data and the same AI.
That architecture has a distinctive shape. Its agent-less framework and open data lake mean security data can be collected without locking the customer into one vendor’s format, and its SIEMless design processes data at the edge, sending only enriched threat signals to the core — the company says this eliminates 98% of the noise, cuts false positives by 55%, and replaces a legacy SIEM in weeks rather than the usual 12 to 24 months, at up to 80% lower total cost of ownership, with no per-gigabyte pricing. For mid-sized enterprises in highly regulated sectors, that is the difference between enterprise-grade defence and no defence at all.
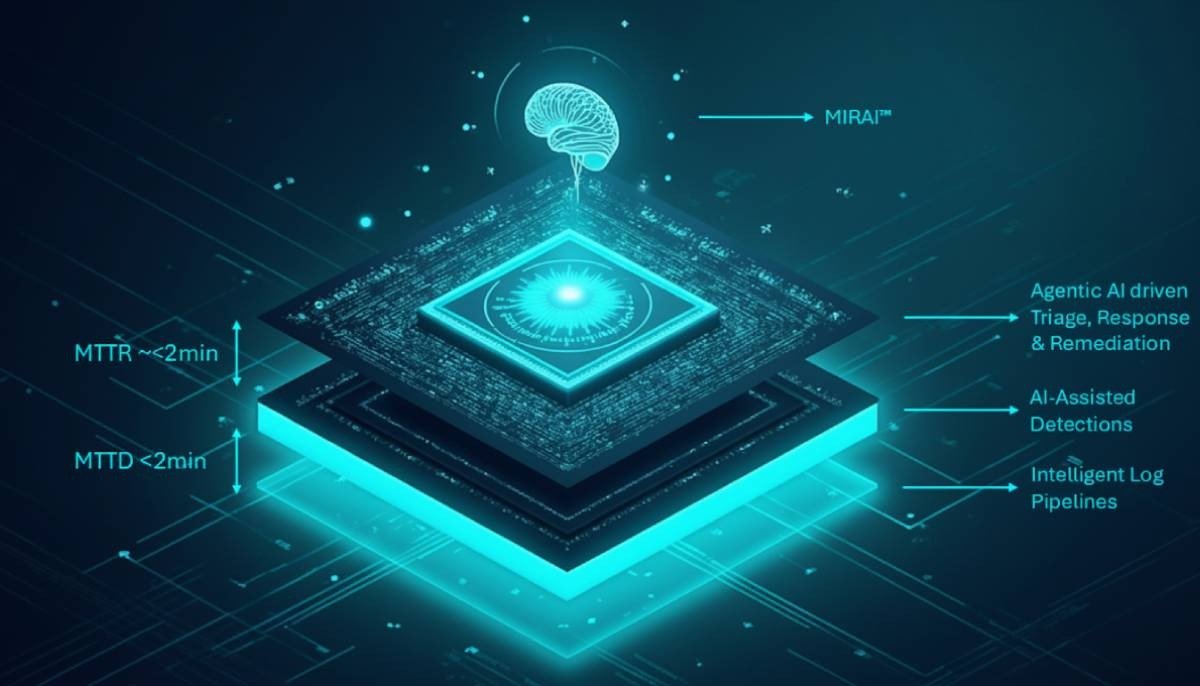
The two-minute promise
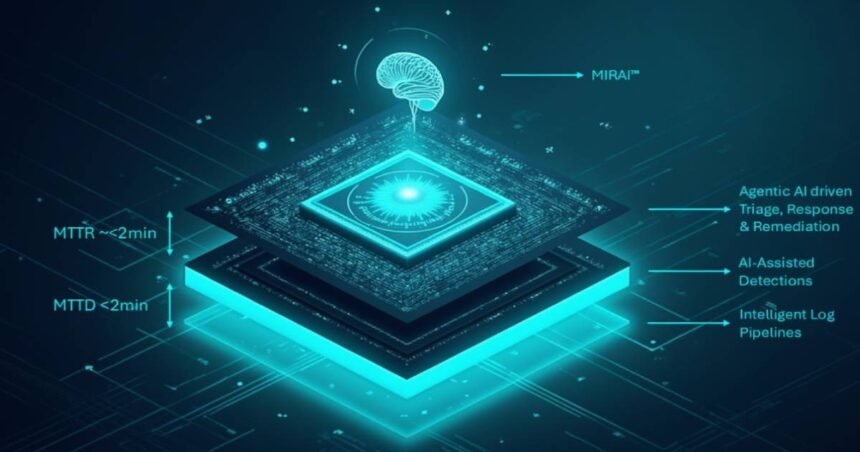
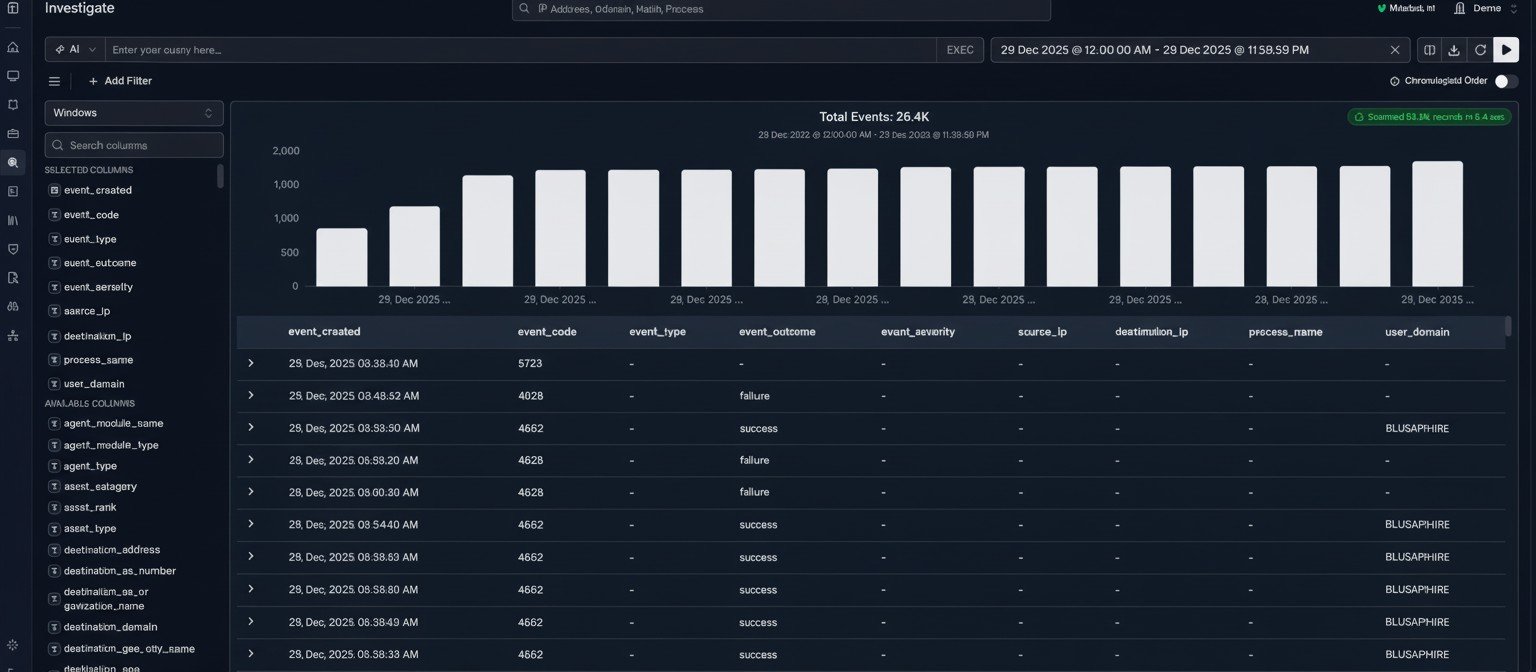
Speed is the headline number. The company says its platform detects threats in under two minutes on average and responds in under four — against an industry-average detection time of 210 days cited in its Nasscom Emerge 50 profile. The engine behind that speed is AR2, its autonomous response and remediation system, powered by the Mirai ReAct framework: it reasons about a threat, plans multi-step remediation and executes it with full explainability, keeping a human in the loop for high-impact actions. Its OneAgent endpoint platform covers more than 400 MITRE ATT&CK techniques, its BluHawk service delivers the same two-minute detection and four-minute response as a fully managed 24/7 SOC, and its DataStreamer gives teams a real-time security data lake without vendor lock-in.
From Hyderabad to the nation
Recognition has followed the engineering. In 2023 BluSapphire was named to Nasscom’s Emerge 50 League of 10 in the cybersecurity category, and the company has raised $9.2 million, including a Series A in 2022 backed by Baring Private Equity Partners India. Its headquarters sits in HITEC City, Hyderabad — the same city where its platform now guards some of India’s most sensitive digital infrastructure.
More Read
The ambition now stretches beyond enterprise security. BluSapphire is extending its platform into Bharat SOC, a national security operations framework that scales the same agentic AI from a central national command down through state, sector and local SOCs, automating the triage of routine alerts so human analysts focus on the threats that matter. It is the same idea that built the company, applied at the scale of a country: one platform, watching everything, answering in minutes.
Why it matters
India is among the most targeted countries in the world for cyberattacks, and every bank, hospital, factory and government office is a potential target — while the defenders are outnumbered and outgunned. BluSapphire matters because it changes the arithmetic for the defenders: a mid-sized enterprise no longer needs a dozen tools and a small army of analysts to see an attack coming, and a nation can imagine a single, coordinated watch over its digital borders. A team from Hyderabad spent a decade building that watchtower, one detection at a time — and now more than 500 enterprises are looking through it.
Keep reading: Hunting the Hunters: Inside FalconFeeds, the Bengaluru Startup Watching 19,000 Cybercriminals in Real Time · The Chip That Learns as It Works: Inside HrdWyr, the Bengaluru Startup Building AI-Native Silicon for the Physical World · More Industrial Automation & Technology stories
Like stories like this? Add Exceptional Technology as a preferred source on Google to see more of our reporting in your search results and Discover feed.