

Picture a customer who opens a savings account at a branch, uses the mobile app, takes a personal loan through an agent, and is offered insurance by a partner. Each of those moments asks for her data, each for a different purpose — and under India’s Digital Personal Data Protection (DPDP) Act, each needs its own clear, provable yes. Now picture her withdrawing one of those yeses in the app on a Sunday night. By Monday morning, the bank has to prove that the marketing team, the agent and the collection agency all got the message. SecureDApp, a Bengaluru security technology company, has just launched the platform built to make that proof a report instead of a week of email threads: SecureCMS, a DPDP consent management platform for banks, non-banking financial companies (NBFCs) and the wider financial sector, launched on 2 November 2026.
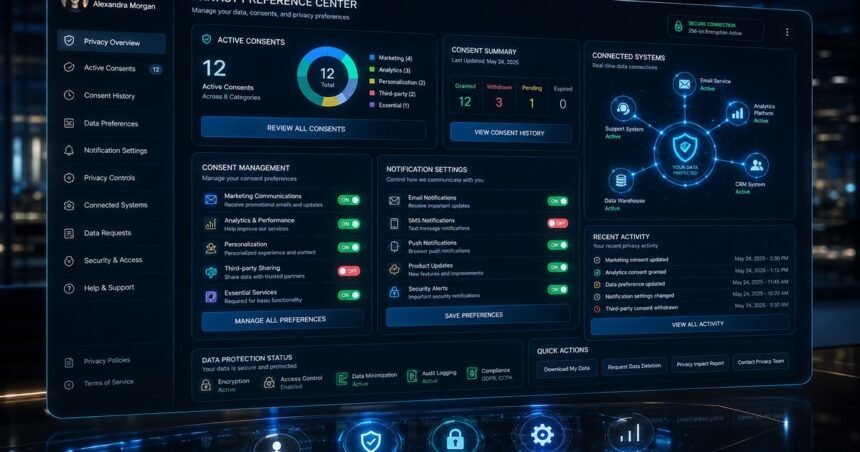
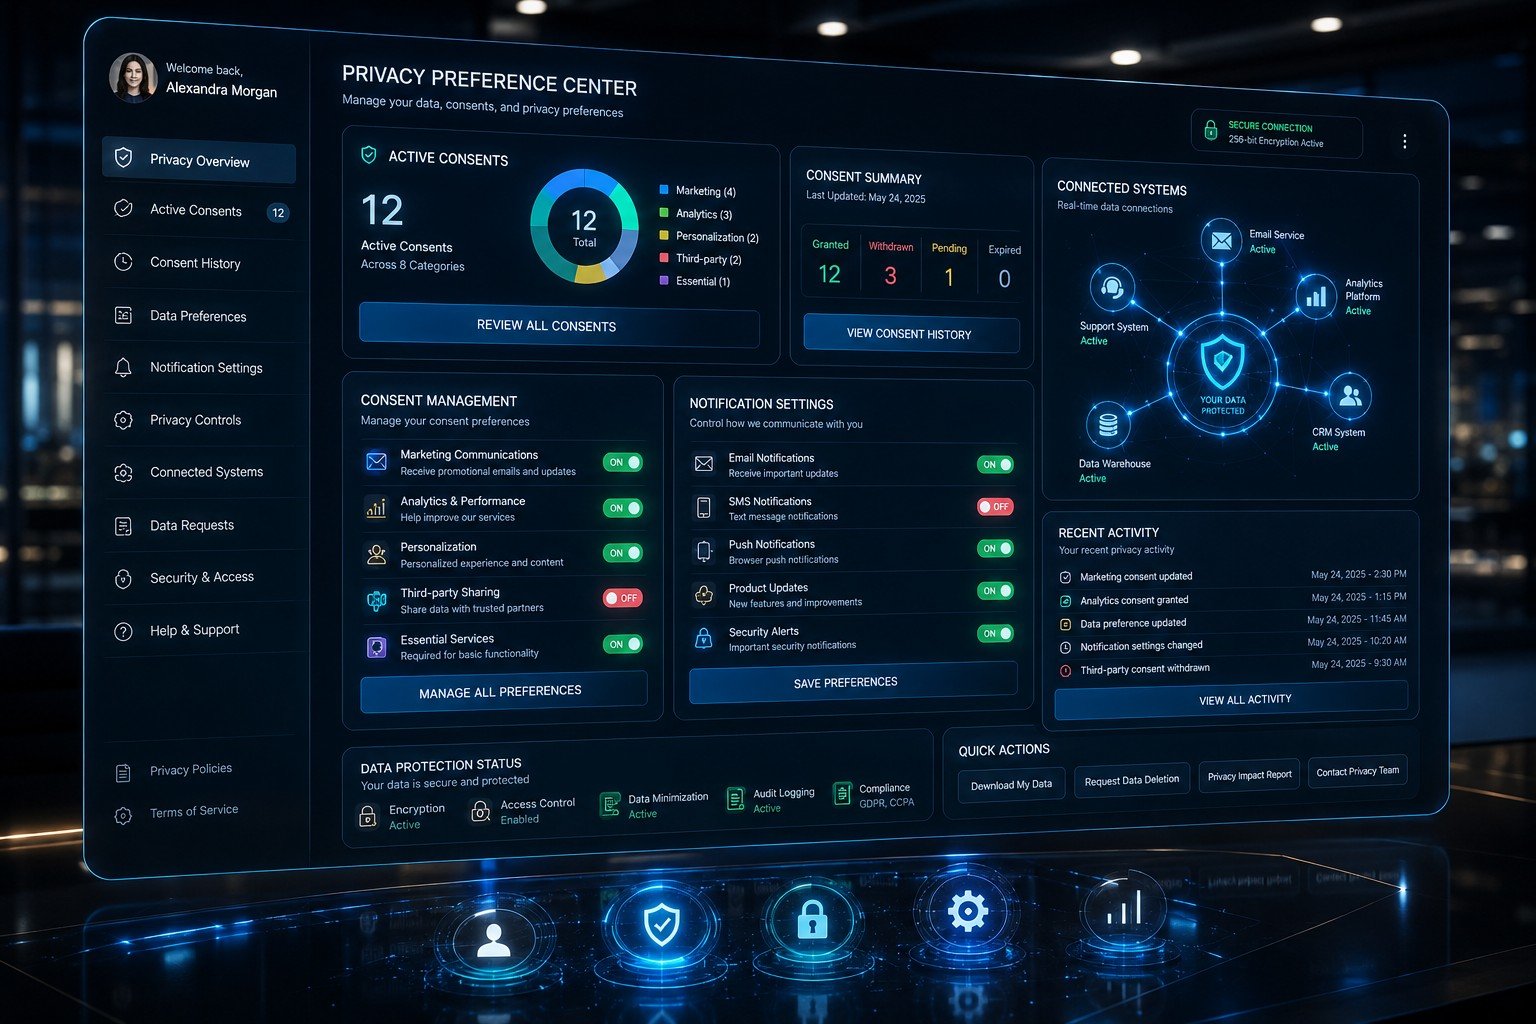 SecureDApp’s consent preference dashboard: active consents, connected systems and purpose-level controls in one place. Image: SecureDApp.
A deadline with teeth
The timing is the story. The Consent Manager provisions of the DPDP Rules, 2025 take effect on 13 November 2026, and the core notice, consent, security and breach obligations follow on 13 May 2027. For lenders, the company says, six months is not much time — because consent in banking is not stored in one place. It is spread across branches, apps, agents, partners and core systems that may be decades old. Under Section 6 of the DPDP Act, consent must be free, specific, informed, unconditional and unambiguous, given through a clear affirmative action and limited to the data actually needed. A single “I agree” at onboarding that covers marketing, cross-selling and partner sharing does not meet that standard, and Section 6(10) places the burden of proof on the business: if a customer says she never agreed to loan offers on WhatsApp, the bank has to show which notice she saw, in which language, on which channel, at what time, and what she did.
The scale makes the record-keeping challenge vivid. The company points to NPCI data showing UPI processed 24.07 billion transactions worth ₹29.37 lakh crore in September 2026, each one touching personal data held by a bank or payment app. It also cites the Reserve Bank of India’s Report on Trend and Progress of Banking in India 2024-25, which put the amount involved in bank frauds at ₹34,771 crore, and CERT-In figures shared in Parliament of 5,70,108 cyber incidents in the banking sector in 2025 and another 3,48,607 in the first half of 2026. And the DPDP Act attaches serious penalties to failures in this area: up to ₹250 crore for failing to take reasonable security safeguards against a breach, up to ₹200 crore for failing to notify the Data Protection Board and affected individuals of a breach, and up to ₹50 crore for other violations including notice and consent failures.
Built for the overlaps, not the cookie banner
SecureCMS was designed around the overlaps between laws rather than around a website cookie banner, and its capabilities show it. The platform records OTP-verified consent at branches, mobile and net banking, direct selling agents, business correspondents, call centres and WhatsApp. It keeps purpose-level records per product, storing the notice version and language, with notices in English and the 22 Eighth Schedule languages. Withdrawals sync in real time to core banking, loan origination, CRM and marketing systems through APIs, webhooks and SDKs, so a withdrawal stops processing within hours rather than weeks.
One of its smartest touches is a legal-hold engine that separates “stop processing” from “erase”. Section 6(4) lets a customer withdraw consent at any time, and withdrawal must be as easy as giving consent — yet the Prevention of Money Laundering Act and RBI’s KYC rules require certain records to be kept for years after a relationship ends. A system that simply deletes data on withdrawal would break one law; one that ignores withdrawal would break another. SecureCMS keeps both duties in view. It also limits data for direct selling agents, collection agencies and other third parties, runs rights requests and grievance workflows with escalation to the Data Protection Officer, and keeps a tamper-evident audit trail that can be exported for auditors or the Data Protection Board.
More Read
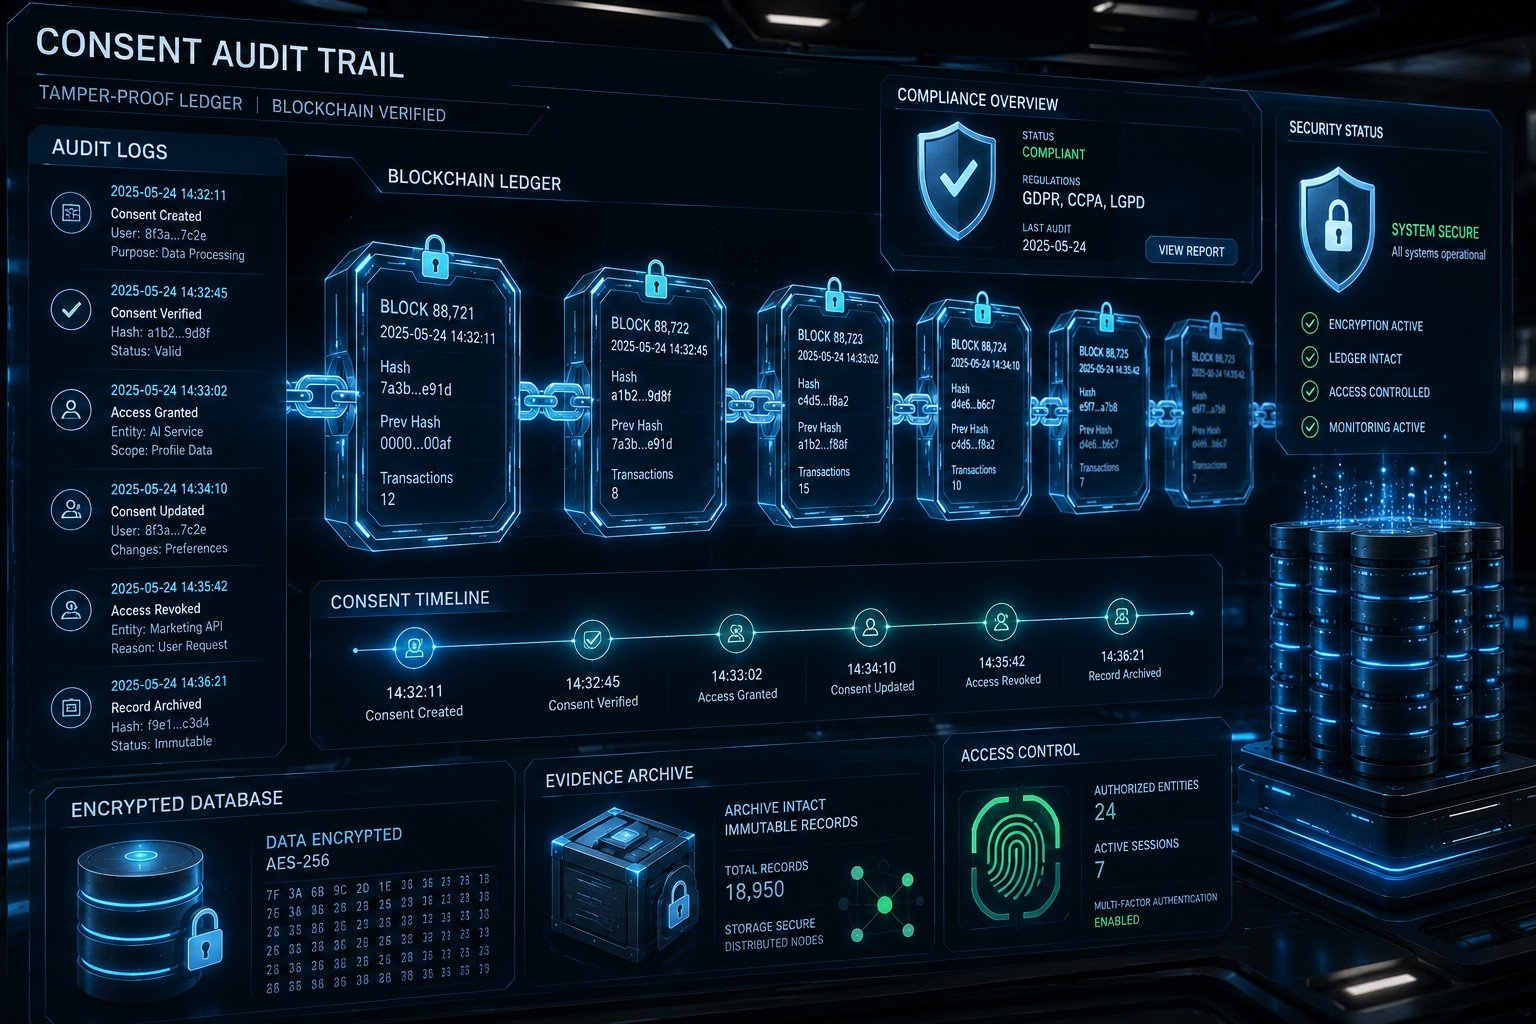 SecureCMS keeps a tamper-evident audit trail of every consent event, so a bank can produce the full history on demand. Image: SecureDApp.
The hardest problem is consistency
“Most banks we speak to are not short of consent forms. They are short of consent records,” said Abhishek Singh, Co-Founder and CEO of SecureDApp. “When a customer withdraws consent in the app on a Sunday night, the question on Monday morning is whether the marketing team, the DSA and the collection agency all know. Under the DPDP Act, the bank has to prove that they did. SecureCMS was built so that answer is a report, not a week of email threads.”
Himanshu Gautam, Co-Founder and CTO, said the hardest engineering problem was not capturing consent but keeping it consistent. “A large bank can have a core banking system, a loan origination system, two CRMs and dozens of partner integrations, all holding copies of the same customer. We treat every consent and withdrawal as an event that each of those systems must acknowledge, and we log the acknowledgement. If one system misses it, the compliance team sees that gap the same day.” That event-and-acknowledgement design is the heart of the platform: consent is not a flag in a CRM, it is a living record with a history, and history is what a regulator will ask for.
One platform, thirteen sectors
The same software runs across 13 industry frameworks, covering fintech, insurance, stock broking, healthcare, ecommerce, SaaS, edtech, schools, telecom, HR and startups as well as banks and NBFCs, each packaging the consent tools that sector needs and mapping where consent applies and where a legal duty applies instead. NBFCs carry an extra layer of their own: the RBI (Digital Lending) Directions, 2025 require need-based data collection with prior, explicit consent and audit trails, with the purpose disclosed at every interaction point and consent granular, including the right to deletion. SecureCMS is also designed to work alongside registered Consent Managers under Rule 4 of the DPDP Rules as that ecosystem forms — it is a consent management platform for a bank’s own operations, working with the independent entities that will register with the Data Protection Board and act for individuals.
SecureDApp itself — Vettedcode Technologies India Pvt. Ltd. — brings a security pedigree to the launch. Its products span smart contract security audits, real-time blockchain threat monitoring, digital signatures and enterprise HSM key management. Gautam, an IIT Kanpur graduate, previously led blockchain engineering teams in India and Singapore and is named on patent filings covering post-quantum secure messaging, digital identity credential verification and cybersecurity threat detection, while SecureDApp’s SecureX DID was a finalist at the Data Security Council of India (DSCI) Grand Challenge 2.0.
It is a deeply Indian engineering story in a new register: not a rocket or a robot, but the quiet infrastructure that lets India’s financial system prove, customer by customer and purpose by purpose, that it asked properly and listened when the answer changed. “May 2027 is not the date to start,” Singh added. “It is the date the Board can start asking questions. The institutions that use the next six months to fix their consent records will spend 2027 serving customers instead of answering notices.” With SecureCMS, SecureDApp is giving those institutions the tool to do exactly that — turning consent from a form filed away into a record that stands up, in every language, on every channel, the same day it is needed.
Keep reading: From Hostel Room to Self-Driving Lab: Inside NovAtom’s AI for Scientific Discovery · The Voice That Speaks Your Language: Inside Vaani’s Self-Serve Platform for India’s Phone Calls · More Industrial Automation & Technology stories
Like stories like this? Add Exceptional Technology as a preferred source on Google to see more of our reporting in your search results and Discover feed.